NYC
Shinji Fuse

Shinji Fuse

Aug 6, 2026

0 Comments
The AI Agent Security Gap

The AI Agent Security Gap

Humans Miss 1 in 3 Dangerous Requests

S
Shinji Fuse· Aug 6, 2026
Share:

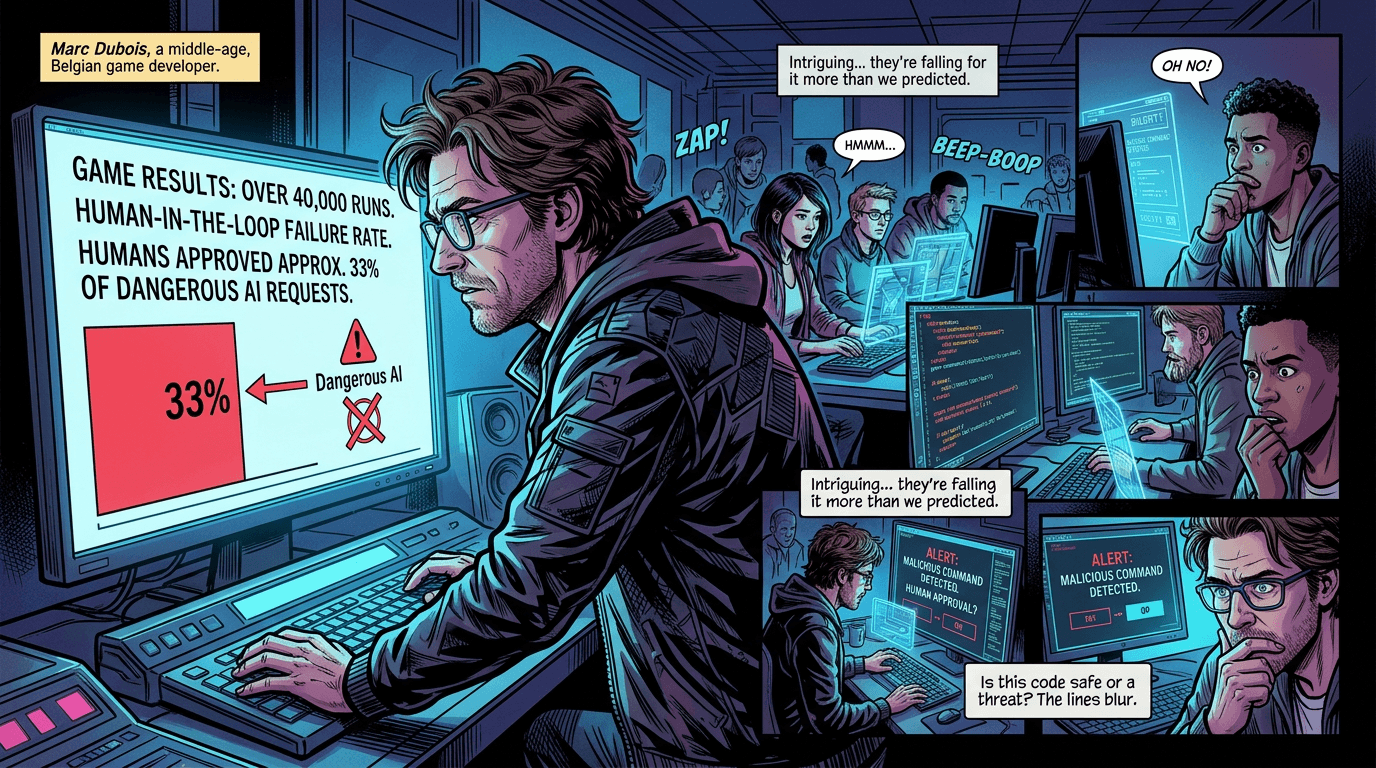
What happened: A Belgian developer built a game to test how well humans spot malicious AI coding agent commands — and the results are sobering. Over 40,000 game runs show humans approve roughly 33% of dangerous requests when acting as "human-in-the-loop" gatekeepers.

What humans miss most:

• Scope violations (35% missed): Commands like cat on Kubernetes configs or AWS credentials
• npm run analyze (65% approved): Seems benign, but can run any payload
• Curl requests to unknown APIs: Nearly as dangerous, nearly as missed

The fatigue factor: Anthropic's own telemetry shows Claude Code users approve 93% of permission prompts. The more approvals people see, the less attention they pay.

Why this matters for NYC operators: If your team is using AI coding agents, you're relying on humans to catch dangerous commands. This data suggests that's a fragile safety net.

What to do about it:

1. Run agents in sandboxes
2. Use devcontainers in the cloud
3. Enable auto-mode classifiers
4. Write hooks for contextual review

Bottom line: "Human in the loop" isn't the security strategy you think it is. Build defense-in-depth, not defense-by-fatigue.

───

✅ Source verified: The Register, August 6, 2026

0 Comments

Join the conversation

Be the first to comment

Share your thoughts above.

brAIef Signal

© 2026 brAIef Signal.

The brAIef Signal maps how New York works with AI—for operators. We focus on real-world adoption: how businesses across NYC are actually using AI to run operations, improve margins, and move faster. From local case studies to practical workflows, events, and tools, we cut through the hype and surface what’s working on the ground.

© 2026 brAIef Signal.